§ 01Overview
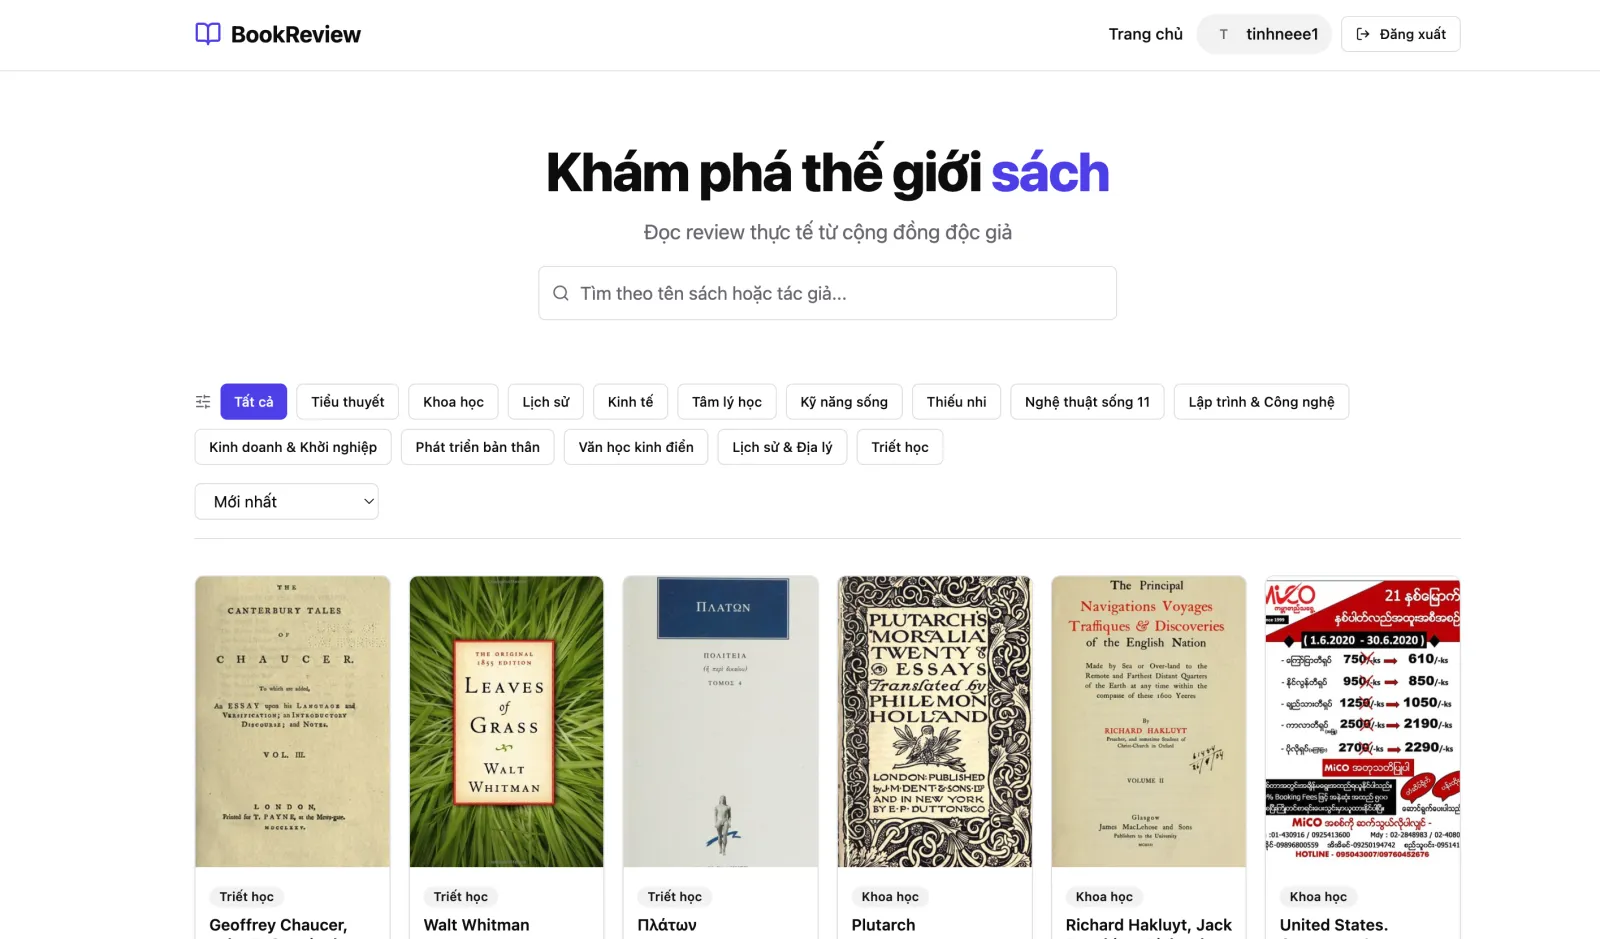
A book catalogue with categories, search and reviews. Anyone can browse; signed-in readers write, edit and like reviews; admins manage the catalogue and moderate content from a dashboard.
The Spring Boot API owns every business rule. The React client stays thin: it renders, caches with TanStack Query and sends a bearer token.
§ 02Problem & solution
Problem
Public reads, authenticated writes and admin-only operations need clearly separated access rules. Reviews and likes touch several tables, and listing pages must stay fast with search and filters.
Solution
A stateless Spring Security filter chain validates JWTs and enforces roles. Services own transaction boundaries, DTOs keep entities off the wire, and a single exception handler returns one consistent error shape.
§ 03My role
Solo developer — API, data model, client. What I personally implemented:
- 01Designed the PostgreSQL schema — users, books, categories, reviews, review likes — and mapped it with Spring Data JPA.
- 02Implemented stateless JWT auth with a custom filter, USER / ADMIN roles, and public GET routes for browsing.
- 03Built paginated, filterable endpoints for books and reviews with a shared page response format.
- 04Avoided N+1 queries when showing which reviews the current user liked by batch-loading liked IDs in one query.
- 05Enforced ownership: users can only edit their own reviews, otherwise the API returns 403.
- 06Built the React + Vite client with TanStack Query, React Hook Form and Zod.
§ 04Architecture
- L1Client
- React + Vite
- TanStack Query
- Axios + JWT
Bearer token on every request - L2Security
- JwtAuthFilter
- SecurityConfig · roles
- CORS
authenticated principal - L3Web
- Auth
- Books
- Categories
- Reviews
- Users
- Health
request DTOs, validated - L4Domain
- Services · @Transactional
- DTOs + validation
- GlobalExceptionHandler
repositories - L5Data
- Spring Data JPA
- PostgreSQL
- GET routes for books, categories and reviews are public; everything else requires a valid token.
- Errors map to typed exceptions (400 / 403 / 404) and one ErrorResponse shape.
§ 05Technology stack
- Backend
- Java 21Spring Boot 3.2Spring SecurityjjwtBean ValidationLombok
- Data
- PostgreSQLSpring Data JPA / Hibernate
- Frontend
- ReactTypeScriptViteTanStack QueryReact RouterReact Hook Form + ZodTailwind CSS
- Tooling
- MavenDocker ComposeHTTP request files
§ 06Key features
- F01
JWT authentication
Register and log in; stateless tokens validated by a custom filter.
- F02
Role-based access
USER and ADMIN roles, with admin-only management endpoints.
- F03
Search & filter
Server-side pagination, text search and category filtering.
- F04
Reviews & likes
Write, edit and like reviews, with ownership checks on edits.
- F05
Admin dashboard
Stats plus management of books, categories, users and reviews.
- F06
Seed & health
Data seeder for local runs and a health endpoint for deployment.
§ 07Engineering challenges
Consistent multi-table writes
Problem
Creating or editing a review also touches counters and like records.
Approach
Keep the whole operation inside one @Transactional service method so any failure rolls everything back.
Likes without N+1
Problem
Showing ‘liked by you’ on a page of reviews can trigger one query per review.
Approach
Collect the page's review IDs and fetch the current user's liked IDs in a single query, then map in memory.
One error contract
Problem
Validation, missing records and permission failures came back in different shapes.
Approach
Typed exceptions plus a global handler that returns the same ErrorResponse for every failure.
§ 08Screens
§ 09Links
- API source (opens in a new tab)github.com/tinhne/book_review
- Client source (opens in a new tab)github.com/tinhne/book-review-frontend
- Live demo (opens in a new tab)book-review-frontend-eta.vercel.app